Walk into your next Salesforce audit with documentation that’s already current.
Most audits start with weeks of rebuilding a picture of the org. aprity keeps that picture current: objects, rules, automations, permissions and integrations, documented in business language and refreshed on every scan.
Read-only accessMetadata purged after each scanEU or US data residency
The baseline is the bottleneck.
You rebuild it every cycle
Last audit’s document is stale. Each new audit starts by re-discovering the org from scratch, the same weeks of work every time.
Evidence is scattered
Rules live in flows, Apex and validation; permissions in profiles and permission sets. Pulling it into one reviewable picture by hand is slow and error-prone.
Automations hide risk
What actually fires on a record, and what blocks it, is hard to see. It is exactly the behaviour an auditor wants explained.
The org, documented before the audit starts.
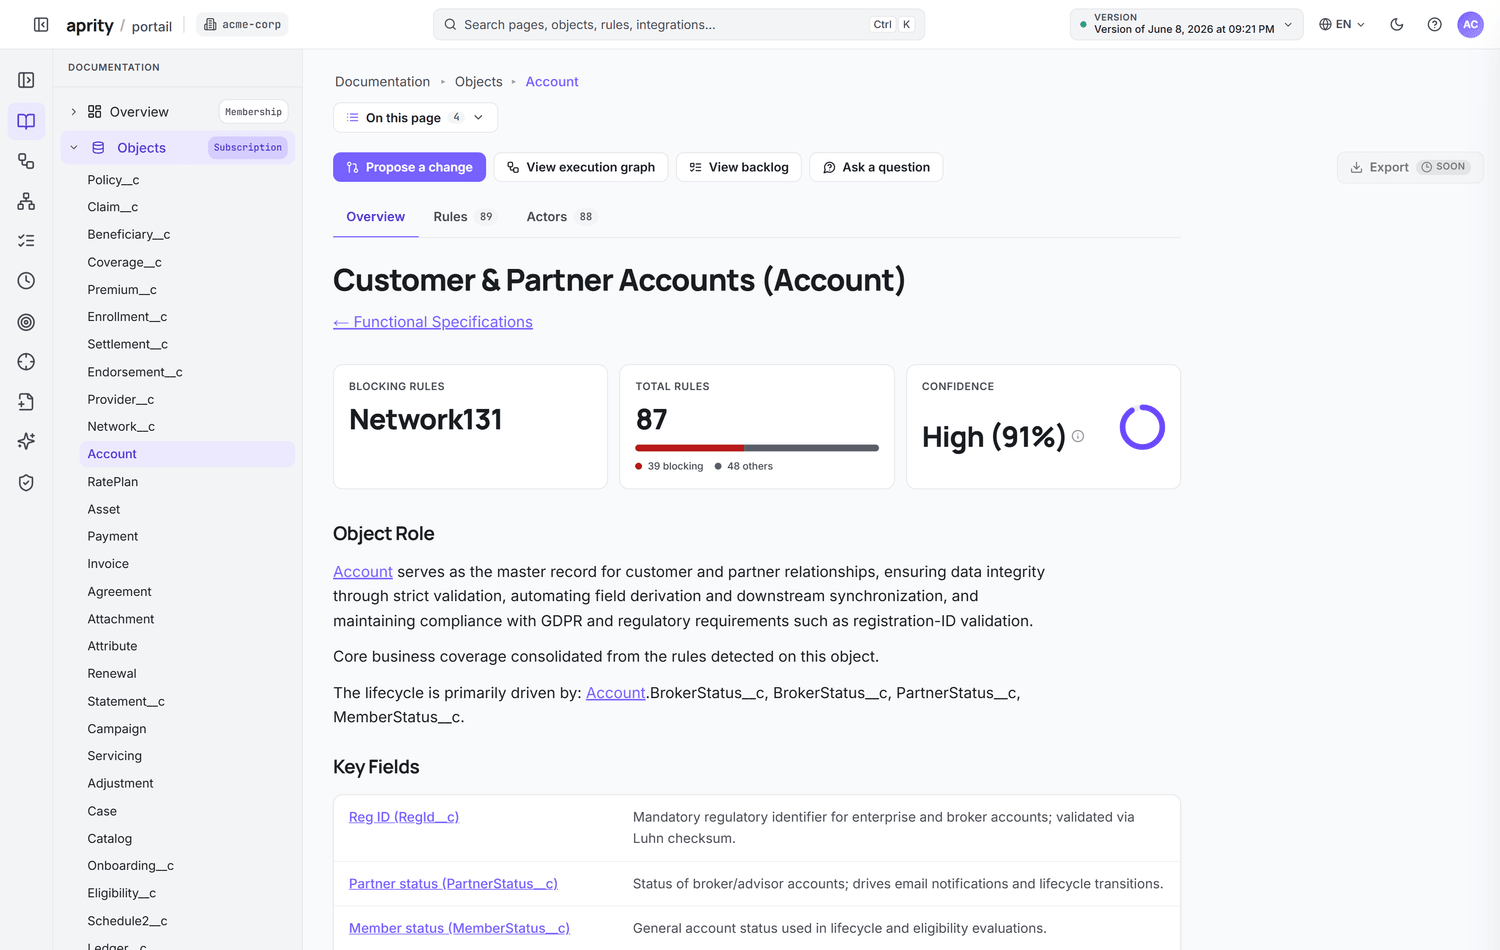
The portal holds the current state of the org in business language. Refresh it with a scan the week of the audit; the auditor reads it, your team does not rebuild it.

Objects, rules and automations
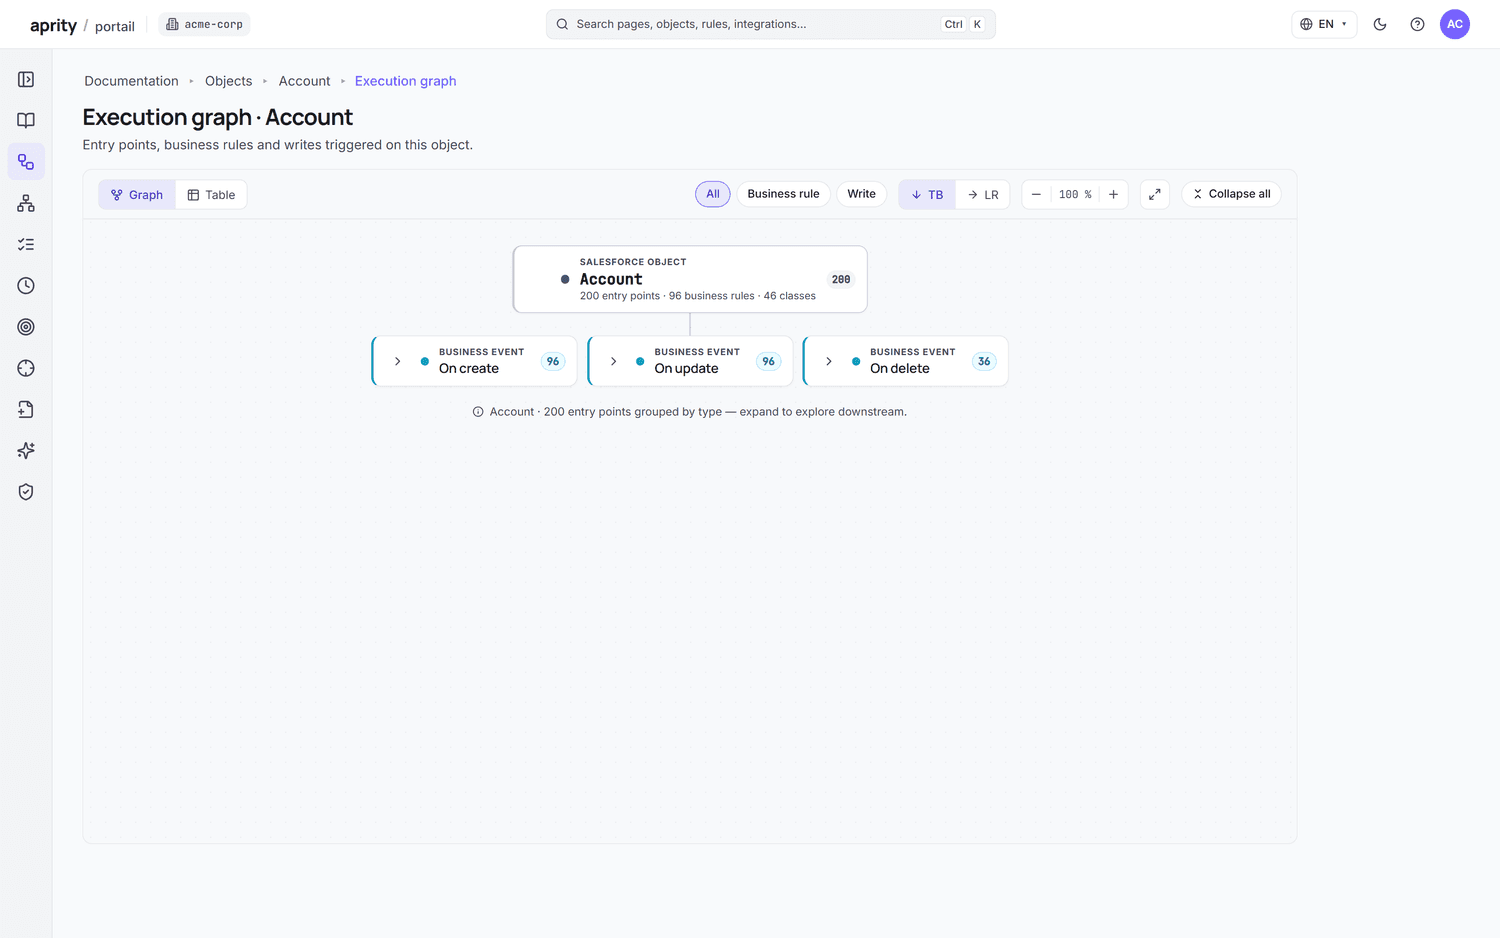
Each object, validation rule, Flow and Apex automation explained in business language, with the component it was read from.
Permissions visibility
Profiles and permission sets surfaced, so access is part of the reviewable picture.
Integrations in and out
Inbound and outbound integrations detected in configuration and code, with the objects they touch.
Change history
Which business rules were added, modified or removed between any two scans: the audit period, in business language.
From certification prep to due diligence.
ISO 27001, SOC 2 and HDS preparation
Keep the Salesforce part of your documentation current, ready when the auditor arrives.
Internal and security review
Give risk and security teams a current map of automations, integrations and access without a manual deep-dive.
M&A due diligence
Hand a buyer or acquirer a current picture of the org instead of a stale slide deck.
ISO 27001, HDS and SOC 2 expect documentation that is kept current. aprity keeps the Salesforce part of it current. It does not hold or grant those certifications, and your team still decides which evidence and controls each audit requires.
A baseline an auditor can check.
A read-only connector reads metadata only, never your records, and raw metadata is purged after each scan. Dependencies and the execution graph are computed from that metadata; the same inputs always give the same result. The AI then explains each object, rule and automation, and each explanation links back to the component it was read from, so an auditor can trace a statement to its source.
Security and trust →- It does not make your organisation ISO 27001, SOC 2 or HDS certified; it documents your Salesforce org.
- It does not audit controls outside Salesforce: your other applications, infrastructure or policies.
- It does not observe runtime behaviour; what the metadata does not describe still needs validation.
- It does not write to the org or read the business data in your records.
Frequently asked questions
Does aprity make my organisation ISO 27001, SOC 2 or HDS certified?
No. aprity does not grant or hold those certifications. It keeps the Salesforce documentation those frameworks expect you to maintain current, so you walk into the audit with it instead of reconstructing it each cycle.
Is the audit baseline actually current?
Every plan includes one scan per week, launched from the aprity app in Salesforce, so you can refresh the baseline the week of the audit. The change history shows which business rules changed between two scans.
Can an auditor trust the documentation?
Dependencies are computed from the metadata and reproducible. Each explanation links back to the component it was read from, so an auditor can trace a statement to its source rather than take it on faith.
Does aprity need write access to run an audit?
No. The connector is strictly read-only and reads metadata only, never the business data in your records. Raw metadata is purged after every scan; only the documentation remains, in the Azure region you choose.
Stop rebuilding the baseline every audit cycle.
Free 14-day trial on your own org. No credit card. Read-only access, and metadata is purged after every scan.
Related
DORA and Salesforce
Document your org's configuration and dependencies for DORA work.
Use caseSalesforce org handover
Map an undocumented org you inherit before you change it.
GuideFind where a Salesforce field is used—and what your search cannot establish.
A blank dependency result is easy to misread as permission to delete a field. A useful investigation instead identifies the proposed change, collects several kinds of evidence and assigns an owner to the gaps.
GlossaryField-level security (FLS)
The Salesforce setting that decides, per profile or permission set, whether a user can read or edit each field of an object.